Short answer: The most practical way to block gambling and betting sites on workplace and guest Wi-Fi is a DNS filter that screens the network's DNS queries against a category list. Because the list is updated regularly, it also catches sites that change their address. Restricting outbound DNS traffic on the firewall and a written usage policy make the block stick.
The line is in the business's name: who carries the risk?
The phone connecting to a betting site may belong to a guest, the computer to an employee; but the IP address seen by the outside world is registered to your business. When an action taken over this line becomes the subject of an investigation, the question is put to the owner of the line first. Identity-matched access records help you show who carried out the action; the filter, meanwhile, prevents such connections from being made in the first place.
The risk takes different forms depending on the sector:
- In factories and on construction sites, shift workers and subcontractor teams use the shared Wi-Fi during breaks; a single widespread habit is reflected in the records of the entire network.
- In cafés and restaurants, customers on match nights may try to open live betting apps over the guest network, while staff carry the risk of using the computer at the till for the same purpose.
- In offices, connecting to suspicious sites from devices that hold payment information, such as accounting or purchasing computers, is a separate danger in terms of information security.
- In hotels, dormitories, and hospitals, young people and children also connect to the guest network; a network open to gambling content directly affects the institution's reputation.
Illegal betting sites are not just a legal matter, either. Some of these sites are intertwined with fake pages that collect personal and payment information, suspicious app downloads, and aggressive redirects. Connecting to these sites from an organization's device also puts the business's information security at risk.
The legal framework
Law No. 5651 (Turkey's Internet Law) provides that access may be blocked to publications for which there is sufficient suspicion that their content constitutes certain crimes. Crimes related to gambling and betting are explicitly included in this list:
"(1) İnternet ortamında yapılan ve içeriği aşağıdaki suçları oluşturduğu hususunda yeterli şüphe sebebi bulunan yayınlarla ilgili olarak içeriğin çıkarılmasına ve/veya erişimin engellenmesine karar verilir: … 7) Kumar oynanması için yer ve imkân sağlama (madde 228), … c) (Ek:25/3/2020-7226/32 md.) 29/4/1959 tarihli ve 7258 sayılı Futbol ve Diğer Spor Müsabakalarında Bahis ve Şans Oyunları Düzenlenmesi Hakkında Kanunda yer alan suçlar."
"(1) A decision shall be made to remove the content and/or block access with regard to publications made on the internet for which there is sufficient reason to suspect that their content constitutes the following crimes: … 7) Providing a place and opportunity for gambling (Article 228), … c) (Added: 25/3/2020-7226/32) The crimes set out in Law No. 7258 dated 29/4/1959 on the Regulation of Betting and Games of Chance in Football and Other Sports Competitions."
Law No. 5651, Article 8/1 (quotation abridged) — mevzuat.gov.tr — unofficial translation
In other words, access to sites with illegal betting and gambling content can be blocked by the competent authorities. These decisions are enforced at the level of internet access providers. For public use providers (toplu kullanım sağlayıcı), however, the Law introduces a separate obligation: all internet public use providers, whether or not they act for commercial purposes, are required to take the measures set by regulation for blocking access to content that constitutes a crime and for keeping access records (Art. 7/2). The Regulation lists the use of a content-filtering system as one of these measures (Art. 4/1-a).
This guide does not provide a legal assessment of any specific incident. For the definitions of the crimes in Law No. 7258 and your business's particular situation, we recommend consulting the official text and your legal counsel. For the scope of the filtering obligation, see the content filtering guide; for the additional rules for places that provide internet for a fee, see the internet cafés page.
Why official blocks are not enough
Illegal betting sites have a well-known behavior: when an address is blocked, a new one opens in its place within a short time. Often a number is added to the end of the same name or the extension is changed; the new address is announced to users through social media accounts, messaging groups, and text messages. It takes time for each new address to be added to the official block list, and the site stays open during that time.
This gap is where a filter working at the network level proves its value. Because category lists are updated regularly, a significant share of new addresses get onto the list quickly. An address you notice yourself can be closed off without waiting by adding it to your own block list. Thanks to matching that also covers subdomains, the different entry addresses of the same site fall under the same rule.
How to block at the network level
There are three common ways to block gambling and betting sites, and each has a different cost:
- A manual address list: Adding addresses one by one to the firewall is possible as a starting point on a small network, but tracking hundreds of thousands of names and constantly changing addresses is practically impossible.
- A firewall web filter: It works with the firewall vendor's category license; it can make decisions at the page level, but it requires a license and configuration.
- A DNS filter: It covers every device on the network, guest phones included, without any installation. The address is withheld the moment the site's name is requested, and the connection never starts. The details of the mechanism are explained in the DNS filtering guide.
For most businesses, the most balanced setup is to enable the DNS filter as the base layer and to use the firewall's web filter, if available, as an additional layer. The block view matters too: on the guest network, a "site not found" answer is quiet and trouble-free; on the organization's devices, a branded block page clearly shows the employee the reason for the block.
Bypass methods and countermeasures
A user with a betting habit may not give up at the first block. Known bypass methods and general countermeasures that can be taken on the network side are as follows:
- Changing the DNS setting manually: If a public DNS resolver is set on the device, queries do not go through the filter. Countermeasure: on the firewall, allow only DNS traffic to your own DNS server and block the rest.
- The browser's encrypted DNS setting: Queries go, encrypted, to an outside resolver. Countermeasure: restrict known encrypted DNS endpoints and turn this setting off centrally on the organization's devices. Details are in the encrypted DNS guide.
- VPN apps: All traffic goes through the tunnel and the DNS filter is bypassed. Countermeasure: you can restrict known VPN traffic with the firewall's application control; but accept that this cannot be fully prevented on a guest network.
- Switching to mobile data: When the user leaves the Wi-Fi and uses their own line, the traffic does not pass through your network. In this case neither your filter nor your records cover that connection; your responsibility is limited to your own line.
Usage policy and communication
A technical block alone does not build a culture. For the staff network, prepare a short written policy explaining the purposes for which the workplace internet may be used, which categories are blocked, and that access is logged under Law No. 5651. This policy can be signed at onboarding and announced together with the privacy notice (KVKK information notice) on the processing of personal data.
The purpose of the policy is not to accuse anyone but to make the rule visible from the start. If blocked attempts are to lead to any conclusion about an employee, this should be handled proportionately within human resources and legal processes. We covered in detail how responsibility is shared for actions an employee takes over the workplace line in the employee internet use guide.
On the guest network, communication happens through the captive portal. The terms of use and a short information note on the login screen tell guests in advance that inappropriate content is blocked and that access is logged. This transparency also greatly reduces complaints from guests who run into a block.
Example: an attempt during a shift break
During a night-shift break at a production facility, a phone connected to the staff Wi-Fi tries to open a newly announced betting address.
Because the name is in the Gambling and Betting category, no DNS answer is given; the attempt is matched to the alias code of the user logged in to the network at that moment.
The scheduled report shows repeated attempts in the same category; management reminds the whole shift of the usage policy without singling anyone out.
- Time
- 02:14:51
- Device
- Factory main firewall — staff network
- Domain
- newbet123.example-domain.example
- Category
- Gambling and Betting
- Who tried?
- vr-3c81d2 → Night-shift staff (probable match)
Blocking gambling and betting with izgate DNS
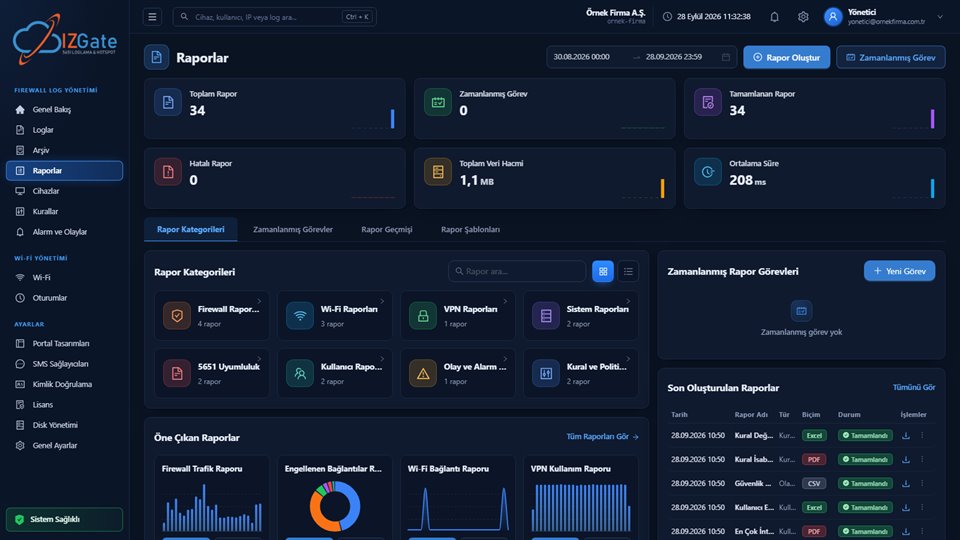
In izgate DNS Security, the Gambling and Betting category is on by default and contains about 279 thousand domain names; the list updates automatically once a day. You can view the category's contents in the panel and turn it off if needed. A new address you notice can be closed off immediately by adding it to your own block list of up to 10,000 names, and a service you want to deliberately allow can be put on the allow list; the allow list takes precedence over categories.
The Blocked screen filters attempts by date range, category, device, and domain name. The "Who tried?" section matches an attempt to the user in your logs: a connection whose log shows the site name is shown as a certain match, and a DNS query made at the same time as a probable match. The Malicious Site Blocking Report can be produced as a PDF with your logo, or as Excel or CSV, and scheduled. On the guest portal, when the filter is connected, an information note stating that harmful and inappropriate content is blocked is shown. All the details are on the DNS Security feature page.
Checklist
- Is the Gambling and Betting category on for both the staff and the guest network?
- Does the firewall block DNS traffic other than to your own DNS server?
- Have known encrypted DNS endpoints been restricted, and the browser setting turned off on the organization's devices?
- Are new betting addresses you notice being added to your own block list?
- Has a written internet usage policy been announced to employees?
- Are the terms of use and the filter notice visible on the guest portal?
- Are you tracking blocked attempts with a regular report?
Frequently asked questions
Isn't access to illegal betting sites already blocked?
Access to sites with illegal betting and gambling content can be blocked by decision of the competent authorities, and these decisions are enforced by access providers. However, such sites frequently come back online at new addresses. A DNS filter on your network that works with a regularly updated category list is an additional layer that narrows this gap.
Does it concern the business if an employee places bets over the workplace internet?
The internet line is registered in the business's name; when an action taken over the line is investigated, the question goes to the business first. Access records help show who carried out the action, while the filter reduces such access from the start. For the legal assessment of a specific incident, we recommend consulting your legal counsel.
What if a guest places bets using their own mobile data?
When a guest leaves the Wi-Fi and uses their own mobile line, the traffic does not pass through your network; neither your filter nor your access records cover that connection. Your network's responsibility is limited to the traffic that passes through your own line.
What should I do if I want to allow a licensed game-of-chance service?
Category lists may not always distinguish a site's license status. If your business wants to deliberately allow a specific service, adding that domain name to the allow list is enough; the allow list takes precedence over categories. The general recommendation for workplace networks is to keep this category fully blocked.
Can a device using a VPN get around the betting block?
Yes. Because a VPN sends all traffic through an encrypted tunnel, it can bypass network-level filters, including the DNS filter. Known VPN traffic can be restricted with the firewall's application control, but you should know that this cannot be fully prevented on a guest network. On the staff network, a written usage policy is the most effective way to close this gap.
This page is for information only; for the current text of the legislation, refer to the official source (mevzuat.gov.tr).
Related guides
What Is DNS Filtering and How Does It Work?
The logic and limits of domain-level blocking.
PracticeEmployee Internet Use: Who Is Responsible?
Records and responsibility on the workplace line.
SetupEncrypted DNS (DoH/DoT) and the Guest Network
Network measures against encrypted DNS that bypasses the filter.